For EXIN-Accredited Training Organizations
Add AI security to your portfolio. Without building a course from scratch.
Give your learners AI security expertise built on the OWASP AI Exchange and aligned with CEN CWA 18398:2026, prEN 18282 and the European e-Competence Framework EN 16234-1.

Sept 2026
Public launch
40 / 90 / 65%
Questions · Minutes · Pass mark
Zero
Candidate prerequisites
300+
EXIN partners worldwide
Bring AI security training to market faster with expert-built content, certification and partner support.

01
Article 4: AI literacy
In force since February 2025. Organisations must ensure staff working with AI systems have demonstrable competence. An attendance record is no longer a strong enough answer for an auditor’s questions.
02
Article 15: Cybersecurity
In force from August 2026. Organisations deploying high-risk AI must evidence cybersecurity competence. Exposure runs up to €15M or 3% of global turnover. DORA and NIS2 pull the same obligations into regulated industries.
In force from August 2026. Organisations deploying high-risk AI must evidence cybersecurity competence. Exposure runs up to €15M or 3% of global turnover. DORA and NIS2 pull the same obligations into regulated industries.
03
Market: the commercial cost is measurable
47% of organisations say missing compliance certification delayed their sales cycles. 38% have lost a deal because they could not evidence security competency. 89% of IT decision-makers prefer certified professionals over academic credentials alone.
04
What this changes for your conversations
Your customers are buying evidence they can put in front of an auditor, an insurer, a board, or a procurement team. They need training for understanding and certification for proof.
Why the training-only solutions underperform
Unbundling looks like a way to win price-sensitive buyers. In practice it lowers average order value, removes your proof of quality, and hands the follow-up revenue to someone else.

01
The exam upsell does not arrive later
Candidates who defer overwhelmingly never come back for it. That uplift is forfeited revenue. If they buy afterwards, they buy direct at full price, and you take none of the margin.
02
An uncertified cohort generates no evidence
No pass rate, badges, or measurable outcome to put in front of the L&D director who signed the purchase order. At renewal you are arguing for a second cohort on the strength of an attendance sheet.
03
Your pass rate makes quality visible
AISP is advanced and scenario-based, with a 65% pass mark drawn from a 200+ page body of knowledge. The exam is where your training quality becomes visible and marketable.
04
Commitment drives completion
Candidates with an exam booked engage differently from day one. That shows up in completion rates, course reviews, and scores, helping you win the next enterprise tender.
05
Badges are distribution you do not pay for
Every certified candidate posts a verifiable, date-stamped credential to LinkedIn. Training-only leaves no trace or referral surface for your marketing team.
EXAM
Independent proof
+
TRAINING
Better understanding
=
PROVEN CANDIDATE
Evidence for requirements
You are not delivering an interpretation of the standard
Most certifications are one organisation’s reading of a framework. AISP is drawn from the actual body of knowledge that helped write the framework. That is a fundamentally different conversation to have with an enterprise client.

The standard:
OWASP AI Exchange
Open, vendor-neutral, 200+ pages, maintained by 165+ practitioners. Contributed 40+ pages directly to the EU AI Act’s security guidance and continues to shape ISO/IEC 27090 and 42001. Referenced by NIST, MITRE, PCI-DSS, and the EU Commission.

The author:
Rob van der Veer
Founder of the OWASP AI Exchange, designer of the AISP courseware and contributor to the development of the exam. Lead author of ISO/IEC 5338, elected co-editor of the EU AI Act security standard, Chief AI Officer at Software Improvement Group, with 34 years in AI, security, and privacy.
The access: no prerequisites
ISACA’s AAISM requires an active CISM or CISSP, which disqualifies many GRC analysts, DPOs, compliance managers, and AI engineers. AISP requires nothing, so every role your client needs certified can sit it on day one.
Domain to obligation mapping
AISP connects practical AI security work to the obligations and standards your clients already need to evidence.
Threat modelling and agentic AI risk
EU AI Act Article 9, risk management
Prompt injection, data poisoning, model exfiltration
Article 15, cybersecurity for high-risk AI
AI red-teaming and adversarial testing
Article 15, robustness
Privacy, compliance, and regulation
Articles 4, 9, 15 and ISO/IEC 42001
AI security controls and the GUARD framework
ISO/IEC 27090 control framework
Organising AI security in the enterprise
Article 9 and ISO/IEC 42001 governance
Where you win against the alternatives
Every major training organisation is now selling some version of AI security. The difference is what they teach and what they are unable to offer.
You have an opportunity to differ here.
ISACA AAISM: governance track
Blocker: requires an active CISM or CISSP. AISP has no prerequisite, so you can serve the whole organisation, not only senior security managers.
CompTIA SecAI+: dual focus
Blocker: splits attention between securing AI systems and using AI for security operations. AISP is entirely focused on securing AI and mapped to European regulatory obligations.
CAISP and DevSecOps: technical track
Blocker: technical depth without the governance dimension, based on the LLM Top 10 rather than the full Exchange. AISP covers both technical and governance in one credential.
Global resellers
Blocker: they hold the delivery relationship, not the curriculum relationship. As an EXIN Accredited Training Organization, you deliver a certification designed by the founder of the standard it is built on.
Start accreditation
The product is already made. Premium option available.
Curriculum development is the expensive, slow part of adding a course. It is already done. Your cost is accreditation and trainer preparation. Your revenue starts with your first cohort.
Ready-to-teach courseware
Designed by Rob van der Veer, with 200+ slides and extensive trainer notes.
Preparation guide and practice
Scenario-based preparation materials and 200 sample exam questions, including 2 sets of 40 and 120 practice questions.
Train-the-trainer
Rich content across 8 video modules, with approximately 6 hours of trainer preparation.
Practical assignments
Three practical assignments to help candidates apply the learning in real scenarios.
Free candidate exam retake
One free retake helps candidates complete the journey with confidence.
Tailored marketing support
AISP APT marketing materials and support for your own commercial offering.
Remote proctoring
EXIN Anywhere supports global virtual cohorts and a consistent exam experience.
Two buyer pools, one accreditation
Corporate cohorts and individual seats open distinct security, L&D, and compliance budgets.
Multi-course accounts are a path, not a one-off
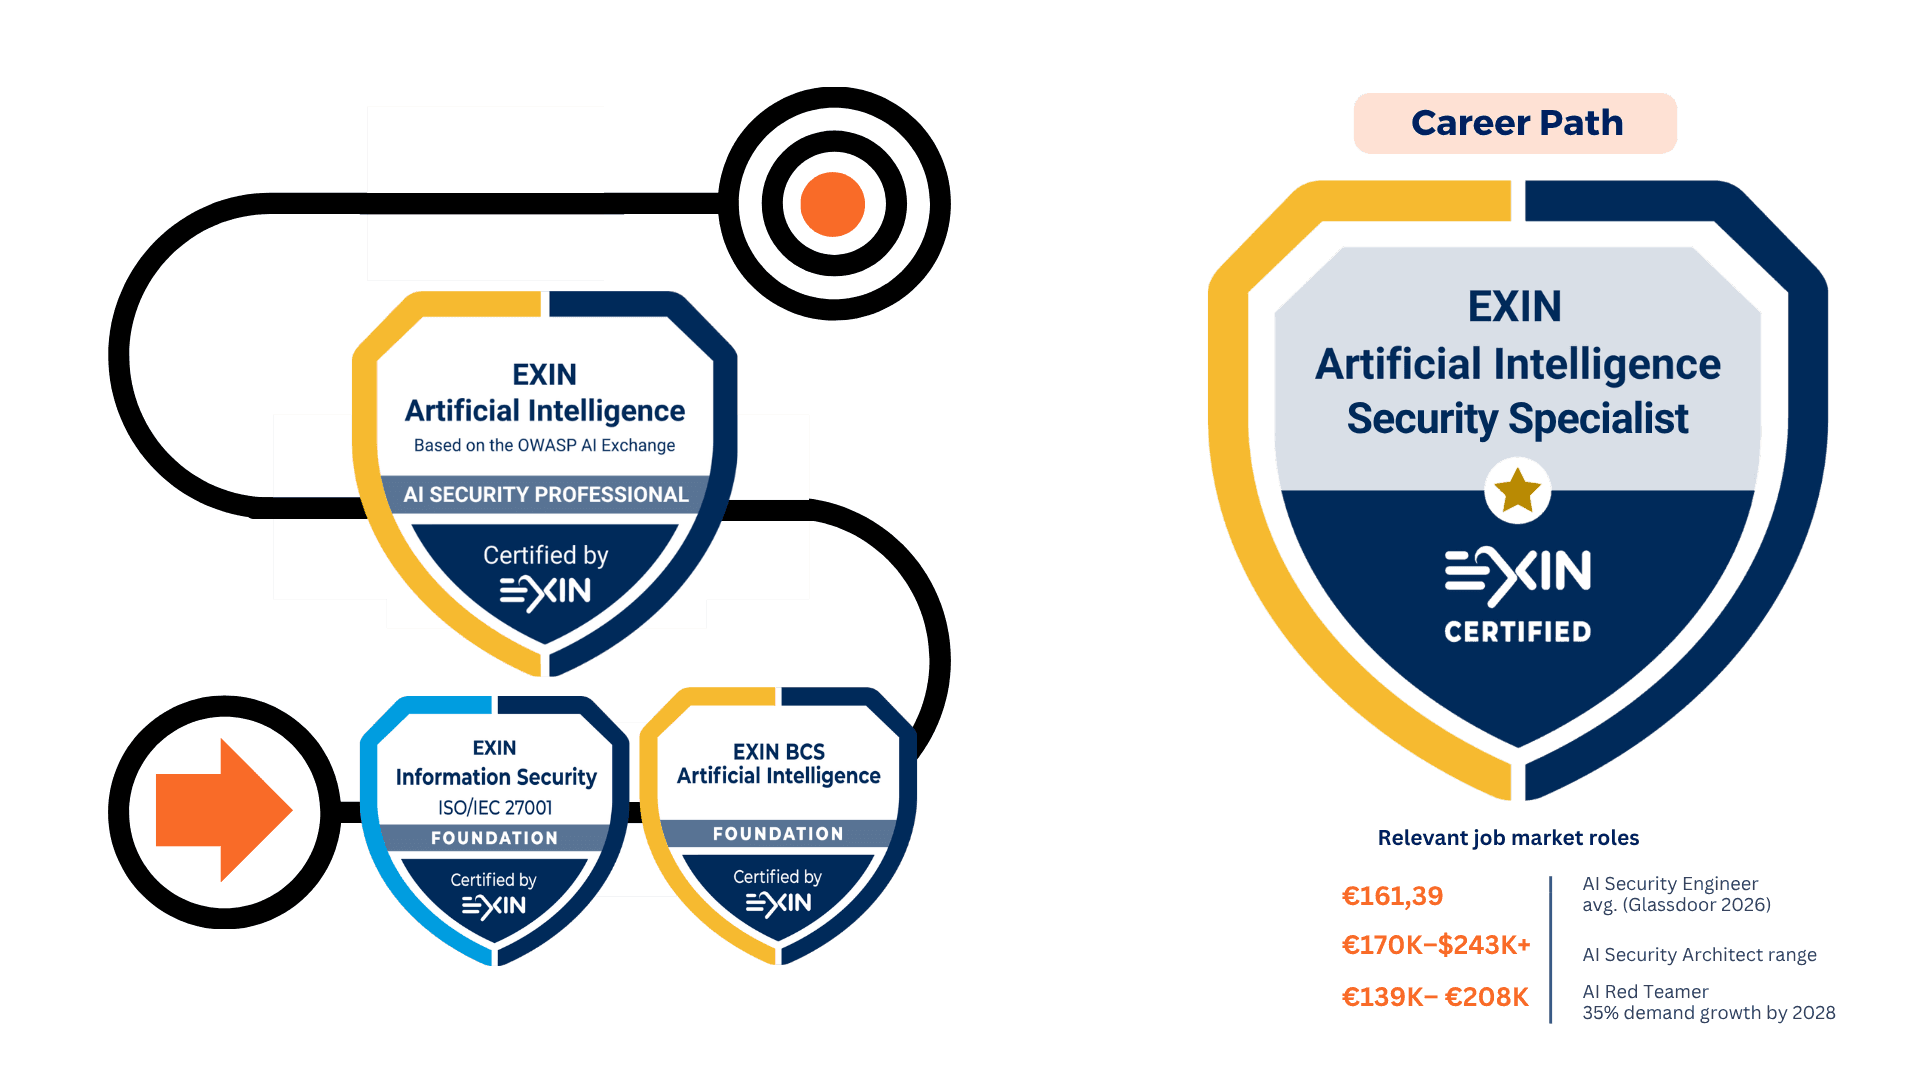
EXIN AI Foundation plus Information Security Foundation lead into AISP, toward the AI Security Manager role. Bundle the pathway and a single course sale becomes a multi-cohort relationship with a measurable career outcome.
AI Foundation
Foundations
→
Information Security Foundation
Security context
→
AISP
AI security proof
How to bring AISP to market
01
Get accredited
Sign a short addendum and follow a fast onboarding process.
02
Deliver the premium option and prep your trainers
Be up and running in weeks, not months. Everything is built for you, from courseware with trainer notes to marketing support.
03
Grow your pipeline
Your AI Foundation and Information Security candidates are natural audiences. AISP reaches security, governance, compliance, and technology roles.
Training plus certification: sell the classroom and the proof
Accrediting your organisation for AISP puts you in market while demand continues to climb. Offer a standard your competitors are not yet claiming.
Start accreditation
300+ partners
40+ years of experience
Over 3 million certified
ISO 27001 certified
OWASP does not endorse individual certification providers. EXIN AI Security Professional is independently developed by EXIN and built on the OWASP AI Exchange body of knowledge. Regulatory references are provided for orientation and are not legal advice. Organisations should confirm their own obligations under the EU AI Act, DORA, and NIS2.