For enterprises and security teams
Your AI systems will be assessed. Can your team prove they’re qualified?
EXIN AI Security Professional certifies that a person can identify, test and govern AI-specific security risk. It is built on the OWASP AI Exchange, the open standard that contributed 40+ pages to the EU AI Act’s own security guidance. Plus, the practitioner who founded it designed the courseware and contributed to the exam development.

Sept 2026 Public launch
Public launch
165+ Practitioners
Built by security experts
40+ pages
Contributed to the EU AI Act
ISO/IEC and EU AI Act aligned
90 min Remote proctored exam
THE OBLIGATION
Attendance records are no longer an adequate answer.
You, like countless companies today, have most likely deployed AI faster than you have built the capability to secure it. That is the normal position. What has changed is that you are now expected to be able to show competence amongst your employees.
01
Article 4 AI literacy, in force since February 2025
Organisations must ensure that staff working with AI systems have demonstrable competence. Internal awareness sessions leave you asserting that competence exists. An independently proctored certification lets you evidence it.
02
Article 15 Cybersecurity for high-risk AI, in force from August 2026
The Act names the threats explicitly: data poisoning, model poisoning, adversarial examples and confidentiality attacks. None of these appear in conventional security certifications.
03
DORA and NIS2 pull the same obligations into regulated industries
Financial services, critical infrastructure and their supply chains face parallel requirements. Regulators are increasingly asking who is formally qualified for AI risk, not who handles security in general.
The practical question: if an auditor, insurer or enterprise customer asked tomorrow who on your team is formally qualified to assess AI risk, what would you send them to prove you’re ready?
EVIDENCE CHAIN
The framework you’ll be assessed against, taught by the people who shaped it
Many available AI security certifications are one organisation’s interpretation of a regulation. AISP sits firmly on an unbroken line drawn directly from the body of knowledge that fed into the regulation itself.
EU AI Act, Article 4
Active
Feb 2, 2025
Curriculum and exam: courseware designed by Rob van der Veer, founder of the OWASP AI Exchange, lead author of ISO/IEC 5338, co-editor of the EU AI Act security standard and Chief AI Officer at Software Improvement Group. Rob also contributed to the exam development.
Active
Aug 2, 2025
Assessment is a scenario-based exam, independently proctored
Imminent
Aug 2, 2026
Each question presents a real system and a real threat and asks for a judgement call. 40 questions, 90 minutes, 65% pass mark, advanced level, delivered remotely through EXIN Anywhere.
Upcoming
Dec 2027 / Aug 2028
Your evidence is a verifiable, date-stamped digital badge authenticated by any third party and traceable back to the same framework your assessors are working from.
Built from practice. Not a committee's interpretation of a regulation.

Built on the
OWASP AI Exchange
Open, vendor-neutral, 200+ pages, maintained by 165+ practitioners. Contributed 40+ pages directly to the EU AI Act’s security guidance and continues to shape ISO/IEC 27090 and 42001. Referenced by NIST, MITRE, PCI-DSS, and the EU Commission.

Courseware designed by
Rob van der Veer
Founder of the OWASP AI Exchange and designer of the AISP courseware. Lead author of ISO/IEC 5338, elected co-editor of the EU AI Act security standard, Chief AI Officer at Software Improvement Group, with 34 years in AI, security, and privacy.
The access: No prerequisites
ISACA’s AAISM requires an active CISM or CISSP, which disqualifies many GRC analysts, DPOs, compliance managers, and AI engineers. AISP requires nothing, so every role your client needs certified can sit it on day one.
THE CAPABILITY GAP
Your security team is skilled.
The challenge is that the threat surface moved.
Conventional certifications have added AI.
Conventional certifications added AI modules because the market asked. Security staff learn threats; governance staff learn policy. The two perspectives rarely meet in one credential. Uniquely, AISP is built around both.
New hires are not the perfect solution
The pool of experienced AI security practitioners is small and expensive. Build formal capability in the professionals you already employ, and be able to demonstrate it.
Regulation is already asking for it
60% of CISOs say their top workforce problem is the wrong skills, not too few people. Meanwhile the EU AI Act, DORA and NIS2 pull AI-specific security obligations into scope. The question arrives before the capability does.
What an EXIN AISP certified professional can do for your company
Every domain maps to real OWASP AI Exchange content, so what your people study for the exam is the same framework they will reference on the job and the same one your assessors are working from.
01
Organizing AI security in the enterprise
Apply the GUARD framework, distinguish AI risk from conventional cyber risk and map training data, models, inputs and outputs to their specific threats.
02
Threat modelling and agentic AI risk
Run AI-specific threat modelling, identify risks in agentic systems and apply repeatable risk treatment and monitoring cycles.
03
Input, development and runtime threats
Classify evasion attacks, distinguish direct from indirect prompt injection and identify data poisoning, model exfiltration and sensitive data leakage.
04
Implementing AI security controls
Apply governance controls across AI, security and compliance programmes; reduce sensitive data exposure and constrain model behaviour.
05
Testing AI systems for security
Distinguish AI red-teaming from conventional testing and run a systematic process from scoping through validation of fixes.
06
Privacy, compliance and regulation
Apply AI-specific privacy principles and map ISO/IEC 23894, 27005, 42001 and 5338 to the EU AI Act, GDPR and emerging copyright risk.
Certify your team
Career impact
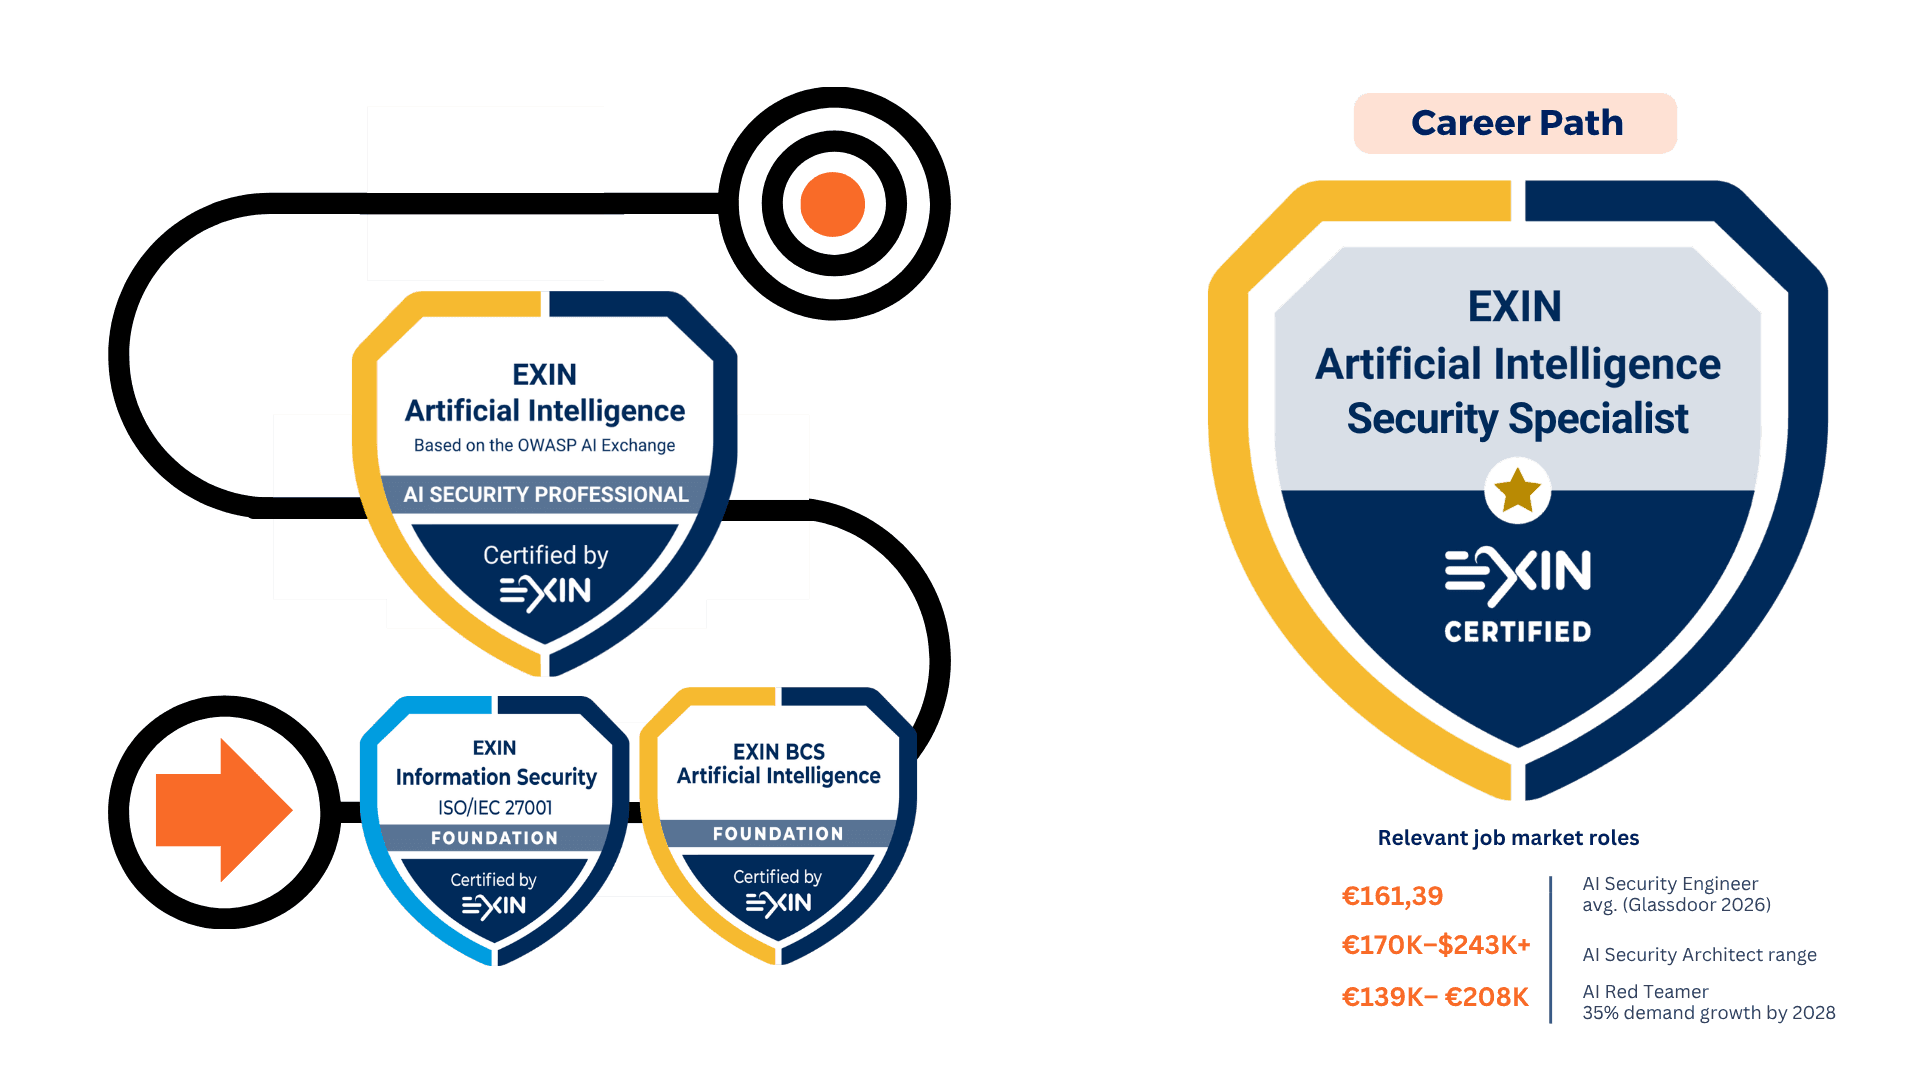
AI Security Specialist: a career path, not just a certification
EXIN certifications connect into real-world job roles. This pathway brings together three certifications, with AISP as the final step, preparing professionals for one of the most in-demand roles in the market.
01
EXIN AI Foundation
Core AI concepts, terminology, and real-world applications
02
EXIN Information Security Foundation
Risk management, access controls, threat landscapes
03
EXIN AI Security Professional
Applied AI security, threat modeling, adversarial attacks, controls, red-teaming, EU AI Act compliance
EXIN AI Security Specialist
One of the most sought-after roles in the market
Every role that touches AI risk is a good fit for AISP. No prerequisite needed.
Security Security professionals
Analysts, architects, GRC specialists, penetration testers and security leaders now responsible for AI systems they were never trained to assess.
Engineering AI and ML engineers
Engineers and data scientists building or deploying AI who need to understand the security implications of the systems they are asked to create.
Assurance Risk, audit and compliance
DPOs, compliance officers and auditors responsible for AI governance, risk management and regulatory readiness under the EU AI Act.
Leadership Technology leaders
Architects, technical leads and decision-makers responsible for evaluating, approving and governing AI deployments across the organisation.
Get your team certified before the market makes it mandatory
AISP launches September 2026. Talk to us about what your next steps look like to certify your in-house team.
Get your team certified